Managed Security Fabric

Network security that thinks faster than threats.

Start with a locked-price Firewall Cleanup on your FortiGate. From there we can move into monitoring and a Fortinet Makeover when the rundown shows what is next. Infrastructure scanning, FortiEDR, and FortiAnalyzer stay available as the program grows.

Security services

Find exposure, then close the response gap.

Infrastructure scanning shows where the risk is. FortiEDR helps contain endpoint threats when patching is not enough, FortiAnalyzer turns firewall and endpoint events into usable evidence, and FortiNAC adds access control where segmentation is needed.

SIEM / analytics

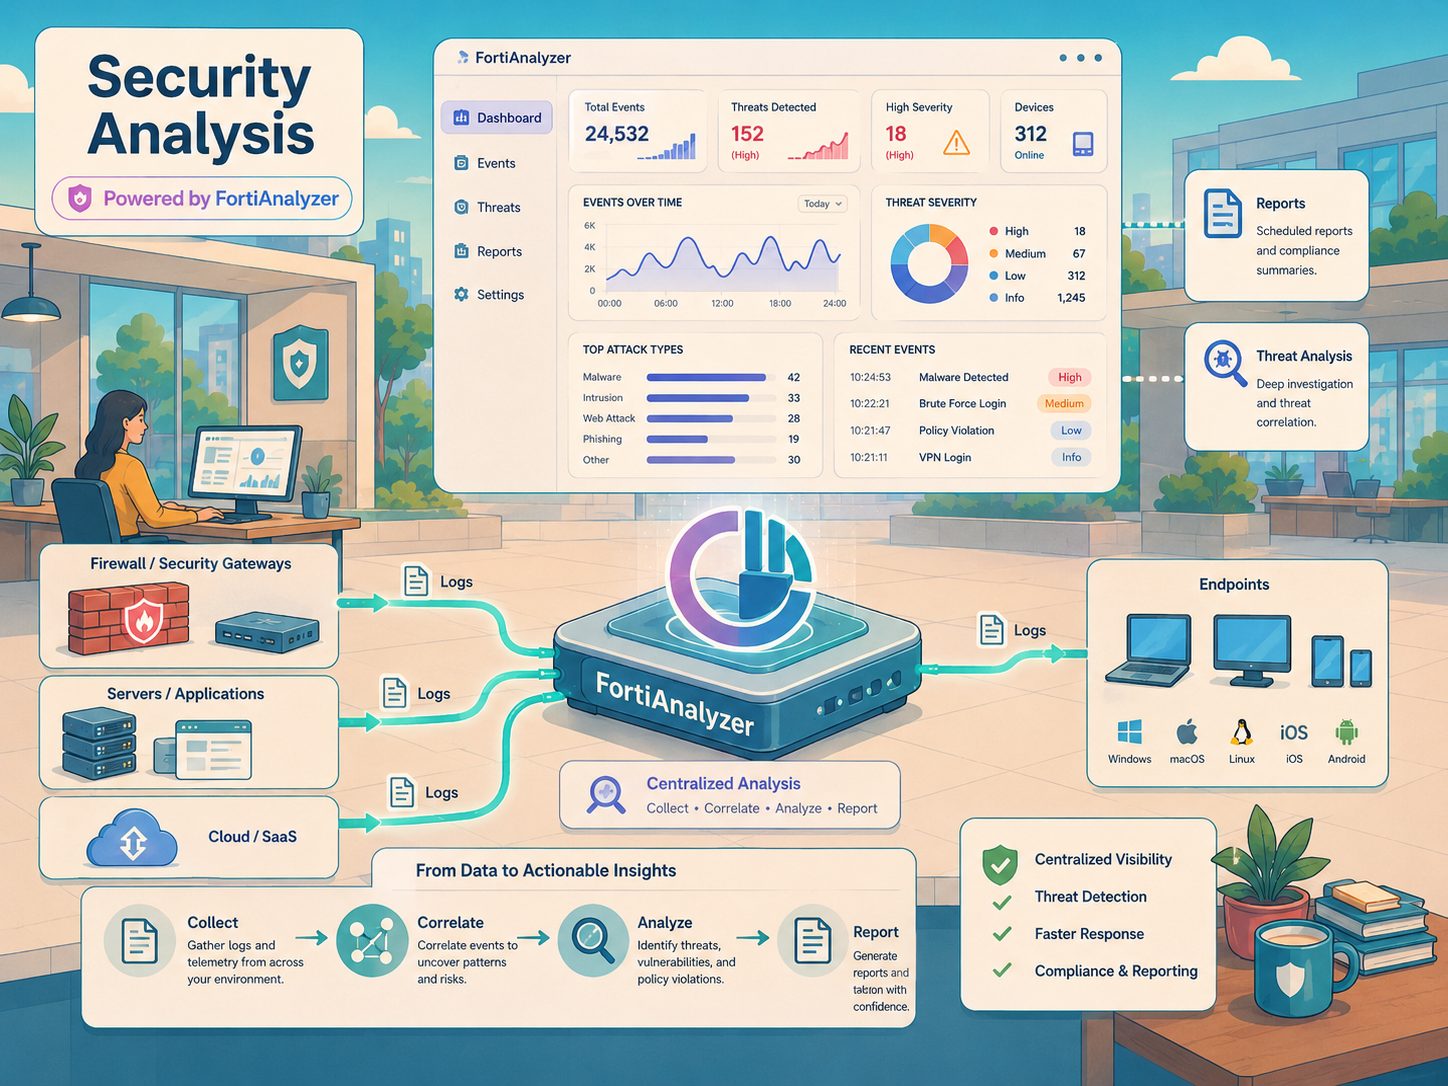
FortiAnalyzer

After the scan shows where exposure exists, FortiAnalyzer becomes the evidence layer for firewall, switch, wireless, endpoint, and third-party security events.

  • Structured dashboards for firewall, IoT, endpoint, and SOC activity.
  • SOAR and XDR workflows with automation packs and AI-assisted queries.
  • Threat intel, IOC services, anomaly detection, and MITRE ATT&CK correlation.
Zero-trust access

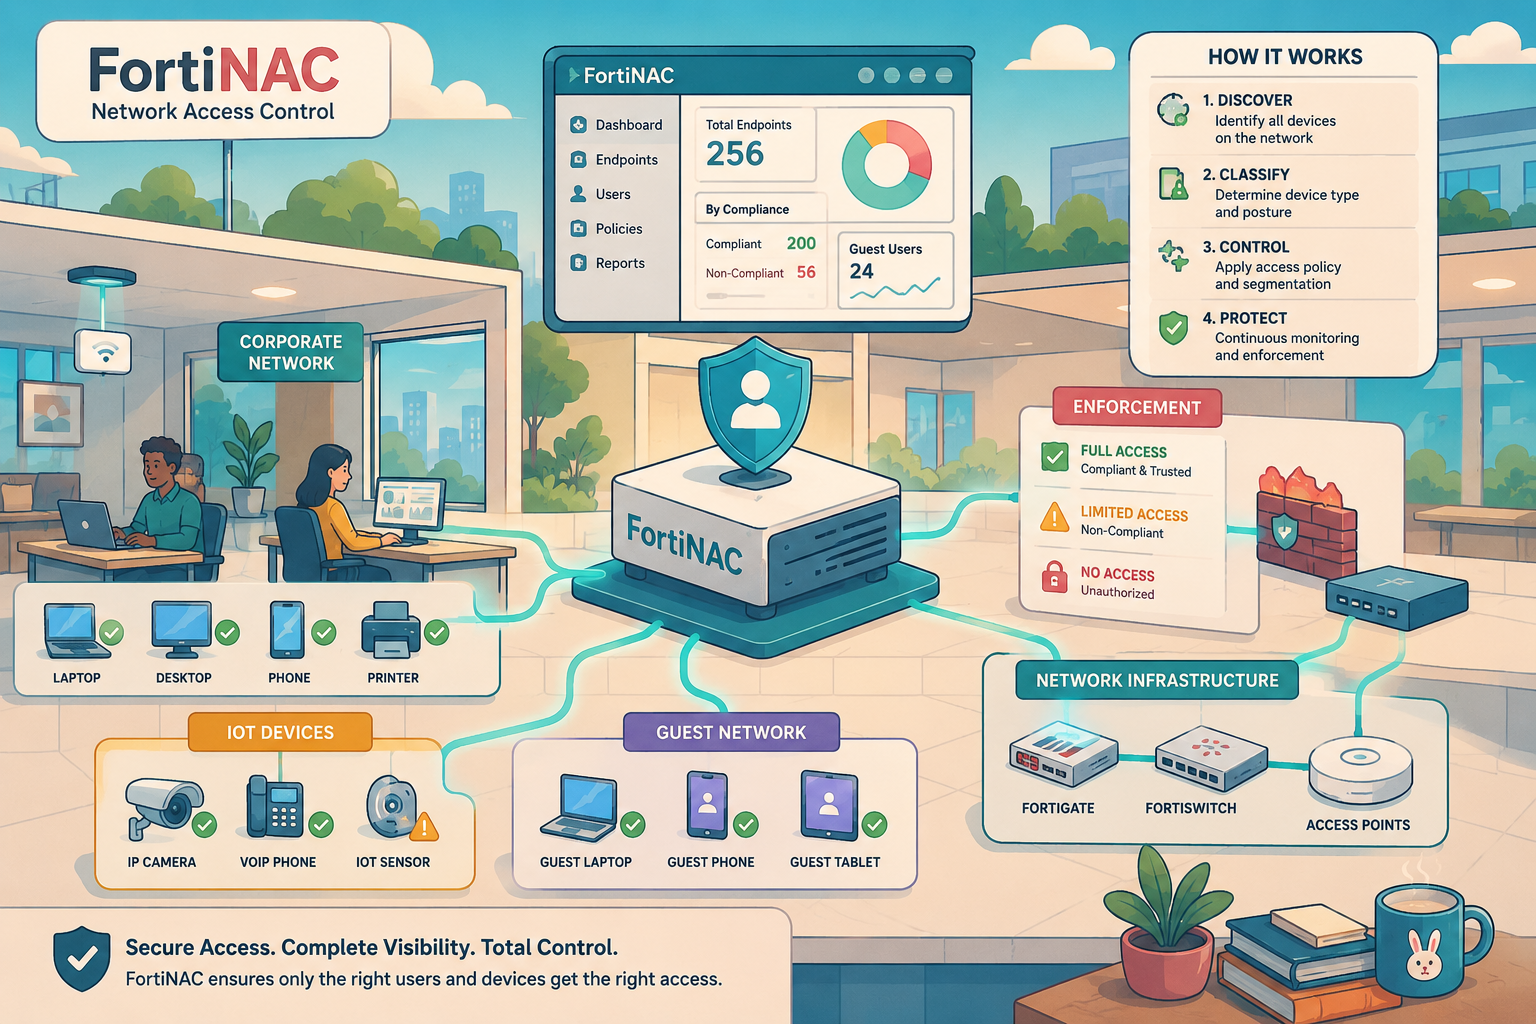
FortiNAC

FortiNAC discovers, profiles, and enforces policy on every device that touches the network, including agentless IoT and OT systems other tools miss.

  • Identity, posture, and risk scoring for every device.
  • Dynamic access policy based on user, device, and network context.
  • Automatic quarantine and remediation for compromised or unknown devices.
Endpoint response

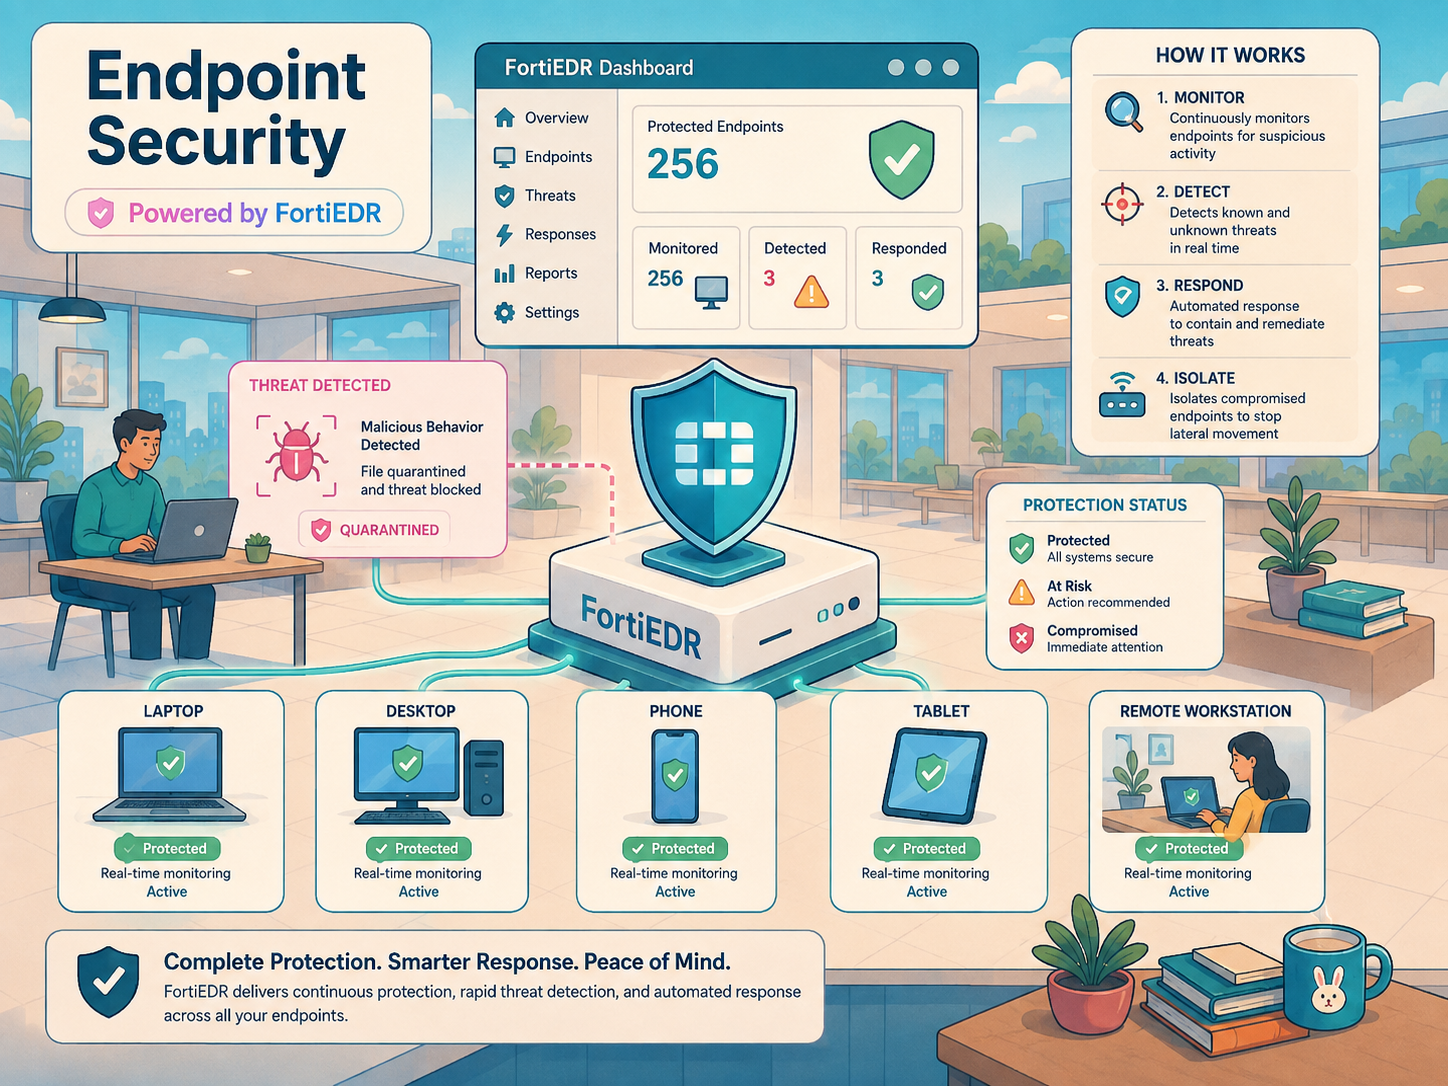
FortiEDR

Vulnerability scans often reveal endpoints that cannot be patched quickly enough. FortiEDR adds detection, containment, and response when exposure reaches the workstation or server layer.

  • Real-time breach prevention with low endpoint overhead.
  • Context-rich events organized by tactic and technique.
  • Automated isolation, domain blocks, file deletion, and password reset workflows.
Vulnerability scanning

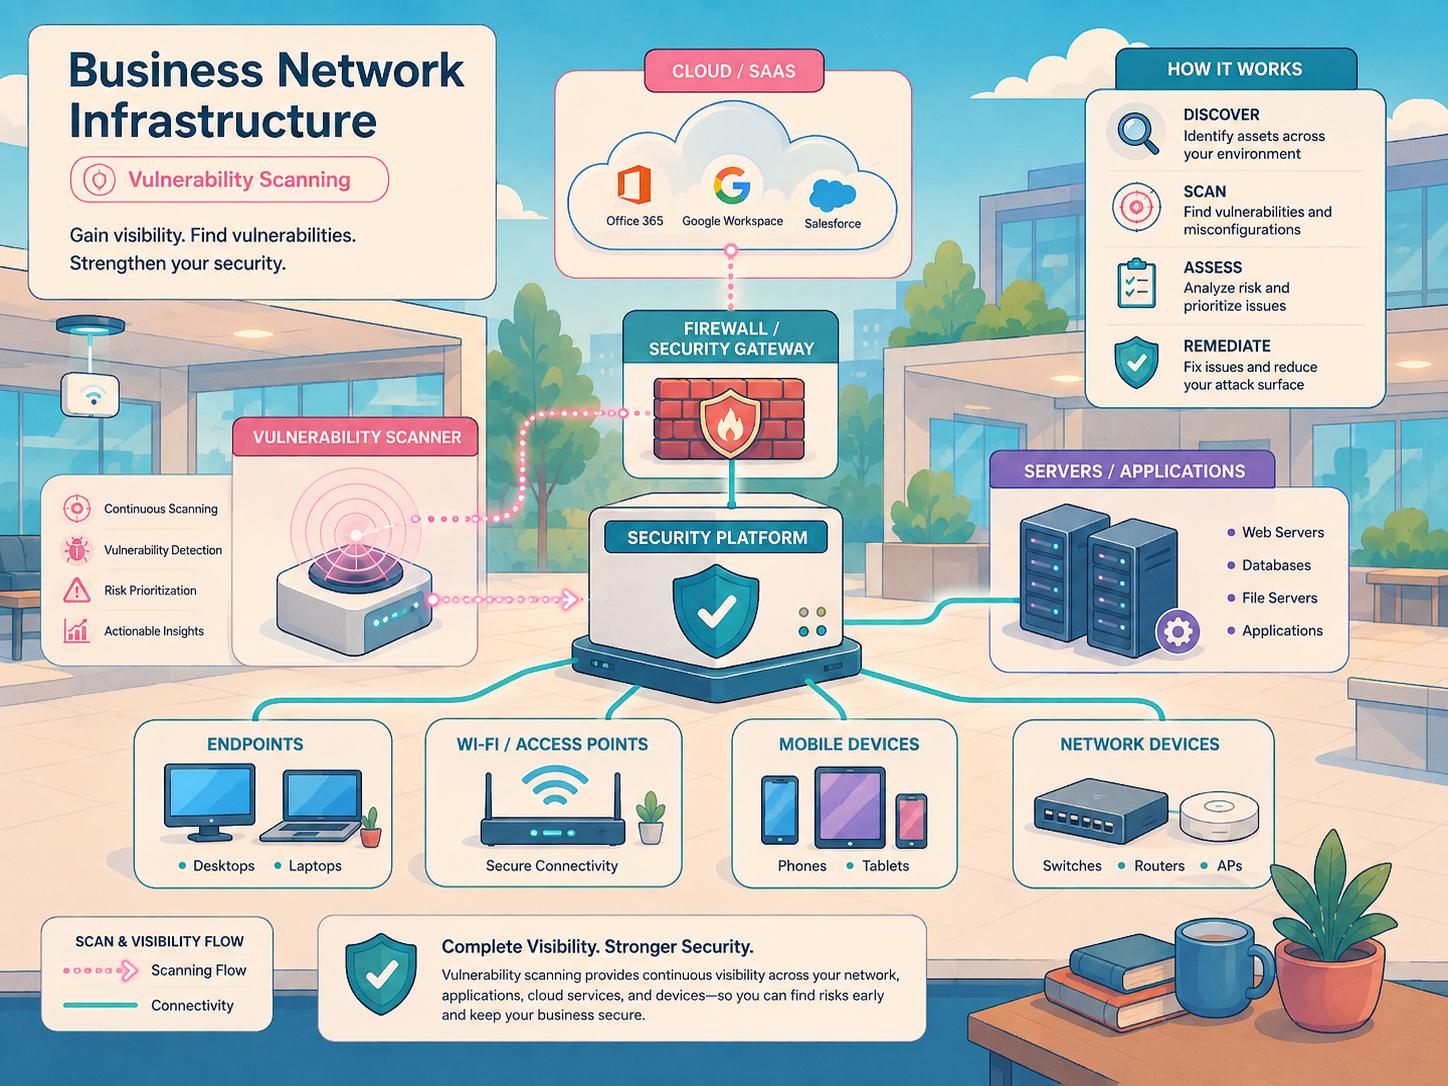
Infrastructure vulnerability scans

We run credentialed and network-based vulnerability scans across your infrastructure to identify exposed services, missing patches, weak configurations, and risky protocols before attackers find them.

  • Internal and external scan scopes for firewalls, switches, servers, endpoints, and cloud-adjacent assets.
  • Prioritized findings with severity, business impact, affected hosts, and recommended remediation steps.
  • Findings become the roadmap for FortiEDR rollout, FortiAnalyzer logging, segmentation, and validation rescans.
Fixed package

Firewall Cleanup — fixed FortiGate package

Start with a locked-price Full Firewall Cleanup on one logical FortiGate (HA counts as one site). Clean the rulebase, fix address objects, and tighten security with a written status rundown — then expand into monitoring and a Fortinet Makeover only when the cleanup proves the need.

  • Full Firewall Cleanup: $4,500 one-time for one logical FortiGate (HA pair at one site = 1). Includes scheduled change window, rollback notes, and documentation handoff. Extra sites and travel are custom / not in package.
  • After cleanup, expand into monitoring and a Fortinet Makeover only when the rundown shows the need.
  • Component SKUs available separately: Rulebase $2,500 · Object hygiene $1,500 · Security tighten-up and status rundown $1,500.

See locked package pricing →

Infrastructure scans

Find exposed risk

Infrastructure scans surface missing patches, weak services, unsupported protocols, and configuration gaps across your infrastructure.

Endpoint response

Turn findings into FortiEDR coverage

High-risk endpoints become candidates for managed FortiEDR deployment, policy tuning, isolation workflows, and response review.

Security analytics

Feed evidence into FortiAnalyzer

Firewall, endpoint, and network telemetry roll into FortiAnalyzer so follow-up reviews are based on usable event context.

Fixed package

Firewall Cleanup — $4,500

Locked-price Full Firewall Cleanup on one logical FortiGate. Clean the firewall first, then grow into monitoring and Makeover when you are ready.

Book Firewall Cleanup →
Segmentation

Contain blast radius

IoT, guests, staff, servers, and sensitive systems get the boundaries they need without breaking daily work.

Response

Alerts with action

Threat alerts route to engineers with context, recommended response, and a path to resolution.

Scan service types

Infrastructure vulnerability scanning scoped to your environment.

Every engagement starts with written authorization, defined scan scope, engineer review, false-positive cleanup, and a prioritized remediation path. Published prices cover common small-business and school environments; larger, multi-site, compliance-driven, or urgent work is quoted after scope review.

External

External Attack Surface Scan

Review your public-facing attack surface, exposed services, firewall edge, remote access paths, DNS, certificates, and internet-reachable infrastructure.

$950+ one-time

Starting scope covers up to 5 public IPs or domains.

  • Written authorization and scope record
  • CVE and exposure review
  • Engineer-verified priority findings
  • Remediation summary
Scope an external scan →
Internal

Internal Infrastructure Scan

Assess internal subnets, VLANs, servers, switches, firewall interfaces, management planes, and credentialed host findings where access is available.

$3,000+ one-time

Starting scope covers up to 75 active assets or 3 VLANs.

  • Internal discovery and scan planning
  • Authenticated scanning where practical
  • False-positive cleanup
  • Prioritized remediation roadmap
Scope an internal scan →
Full assessment

Full Infrastructure Assessment

Combine external and internal scanning with deeper engineer review, executive reporting, remediation planning, and validation after fixes.

$6,500+ one-time

Starting scope covers up to 150 active assets and includes one validation rescan.

  • External and internal coverage
  • Credentialed scan support
  • Executive and technical reports
  • Fix validation and next-step planning
Scope a full assessment →
Fixed package

Firewall Cleanup — locked FortiGate package pricing.

Book a Full Firewall Cleanup on one logical FortiGate. When the status rundown shows what is next, we can expand into monitoring and a Fortinet Makeover.

Package hero

Full Firewall Cleanup

All three components on one logical FortiGate: rulebase cleanup, address object hygiene, and security tighten-up with a written status rundown.

$4,500 one-time

One logical FortiGate (HA pair at one site = 1). Multi-FG billed qty × $4,500 — no fixed multi-packs.

  • One logical FortiGate (HA pair at one site = 1)
  • Scheduled change window
  • Rollback notes
  • Documentation handoff
  • Rulebase cleanup, address object hygiene, and security tighten-up and status rundown
  • Clear next steps toward monitoring and Makeover

Custom / not in package: extra sites and travel. Probe / monitoring onboarding is separate — not inside Cleanup.

Book Full Firewall Cleanup →
Policy cleanup

Rulebase cleanup

Review and clean FortiGate policies so every rule has clear intent, current sources and destinations, and no dead weight.

$2,500 one-time

One FortiGate with a typical SMB/school rulebase.

  • Unused, shadowed, and duplicate rule removal
  • Any/any and overly broad allow reviews
  • Logging and hit-count sanity checks
  • Business-intent notes on remaining policies
Book Rulebase cleanup →
Objects and naming

Address object hygiene

Fix address objects, groups, and naming so the firewall is readable for the next change window and the next engineer.

$1,500 one-time

One FortiGate object table.

  • Consistent naming for hosts, networks, and groups
  • Duplicate and orphaned object cleanup
  • Alignment to real VLANs, servers, and services
  • Service object and VIP review where needed
Book Address object hygiene →
Tighten-up

Security tighten-up and status rundown

Close obvious hardening gaps and deliver a plain-language status of the firewall — what is solid, what is risky, and what to do next.

$1,500 one-time

Written status rundown for one FortiGate.

  • Admin access, interfaces, and profile hardening checks
  • VPN, NAT, and insecure protocol review
  • Written firewall status rundown
  • Prioritized next steps toward monitoring and Makeover
Book Security tighten-up →

Multi-FortiGate sites: Full Firewall Cleanup is qty × $4,500 per logical FG (HA pair at one site = 1). No fixed multi-FG packs. Extra sites and travel are custom. Probe / monitoring onboarding is separate. Path after cleanup: monitoring, then Fortinet Makeover scoped from the rundown — contact cleveston@databunnyllc.org.

Secure your network

Tell us what you are running and what you need to protect.

We will come back with a scoped Security Fabric plan covering the right tools for your environment. No sales reps - you talk to the engineer.